Enter your keyword

Blog

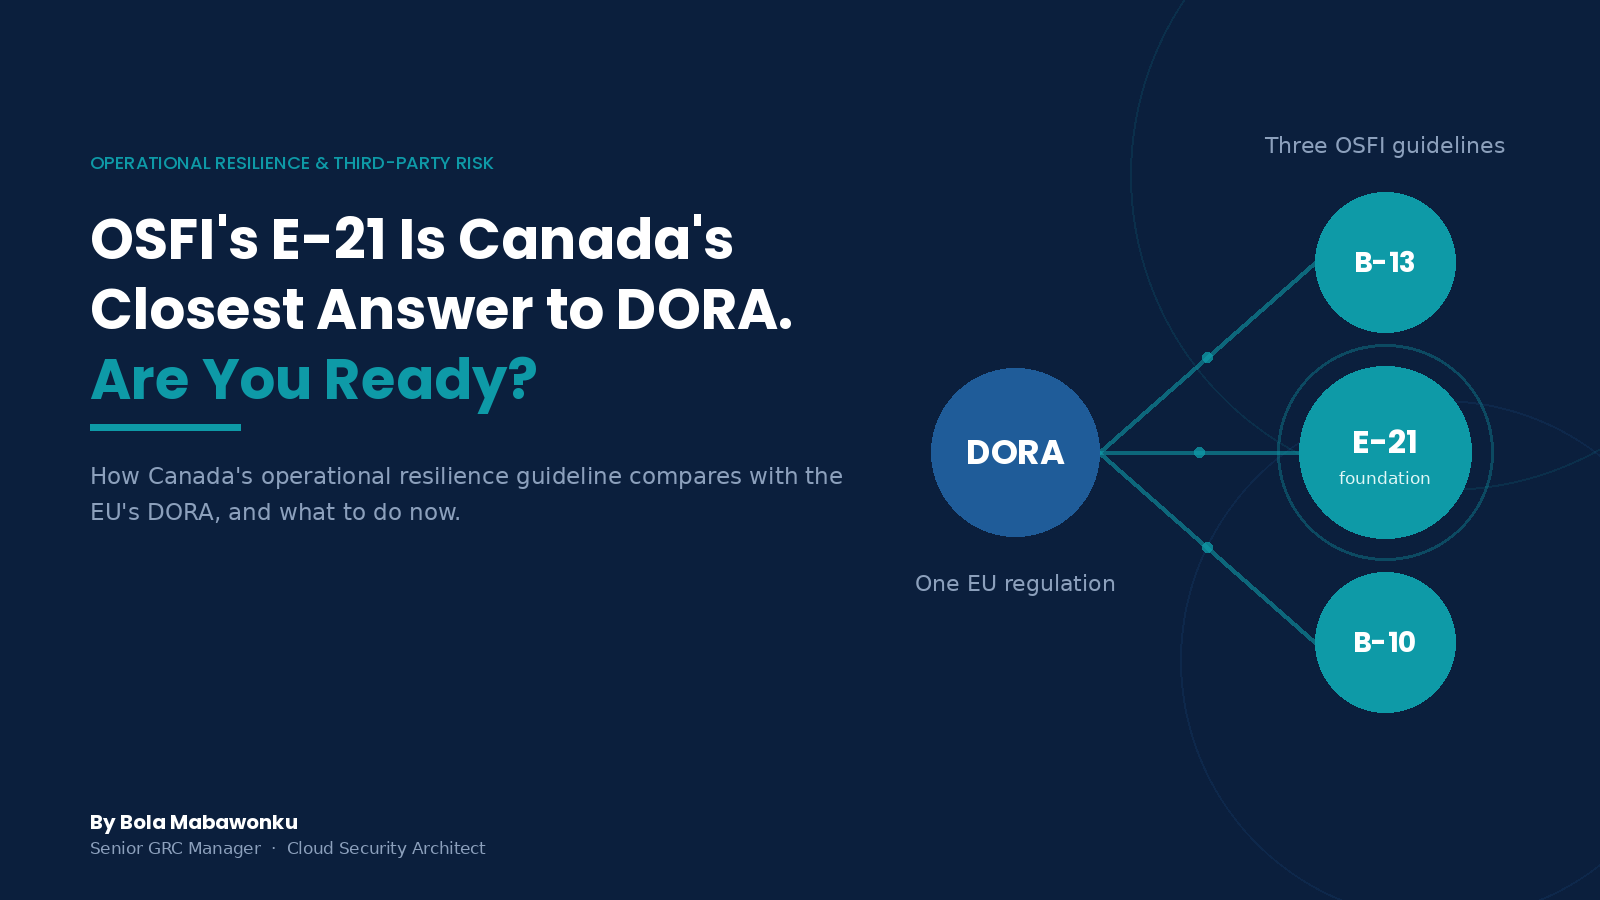
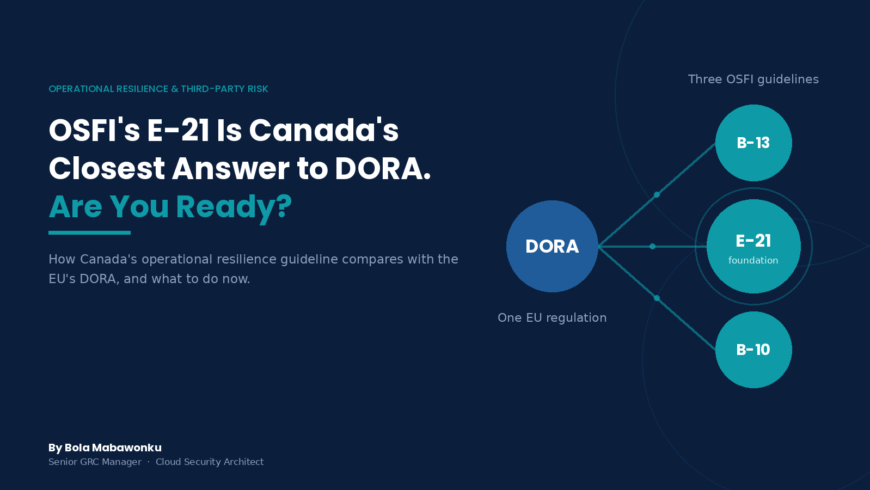
DORA Has a Canadian Cousin. Is Your Resilience Program Ready?

DORA Has a Canadian Cousin. Is Your Resilience Program Ready?

Abstract On September 1, 2026, the Office of the Superintendent of Financial Institutions (OSFI) expected federally regulated financial institutions (FRFIs) to reach full adherence with Guideline E-21, Operational Risk Management and Resilience. E-21 is often described as Canada’s answer to the European Union’s (EU) Digital Operational Resilience Act (DORA), and this article tests that comparison. […]
The SEC Cybersecurity Disclosure Rules One Year On: What Security Leaders Still Have Wrong

The SEC Cybersecurity Disclosure Rules One Year On: What Security Leaders Still Have Wrong

The SEC’s cybersecurity disclosure rules have been in effect since December 2023. We now have over a year of real-world implementation experience, real 8-K filings from companies responding to material cybersecurity incidents, and a clearer picture of where organizations are falling short. The answer, in my observation, is consistently the same place: they are treating […]

AI Is Using Your Data. Are You Aware?

AI Is Using Your Data. Are You Aware?

Abstract AI systems are only as trustworthy as the data governance underneath them, and most organizations have not done the foundational work of inventory, classification, and access control before connecting AI tools to their environments. This gap is driving a measurable rise in shadow AI incidents and breach costs, and it now extends into overlooked […]

Cloud IAM and Zero Trust: Why Least-Privilege Is Still the Hardest Problem in Cloud Security

Cloud IAM and Zero Trust: Why Least-Privilege Is Still the Hardest Problem in Cloud Security

Cloud IAM and Zero Trust: Why Least-Privilege Is Still the Hardest Problem in Cloud Security After a decade of zero trust as the dominant security philosophy, identity and access management remains the most commonly exploited attack vector. Here is why — and what actually works. Bola Mabawonku  ·  Senior GRC Manager & Cloud Security Architect  […]

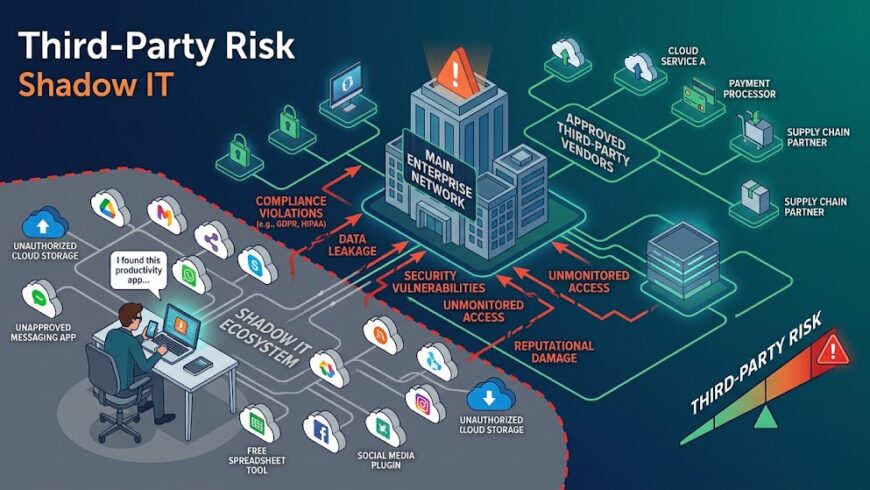
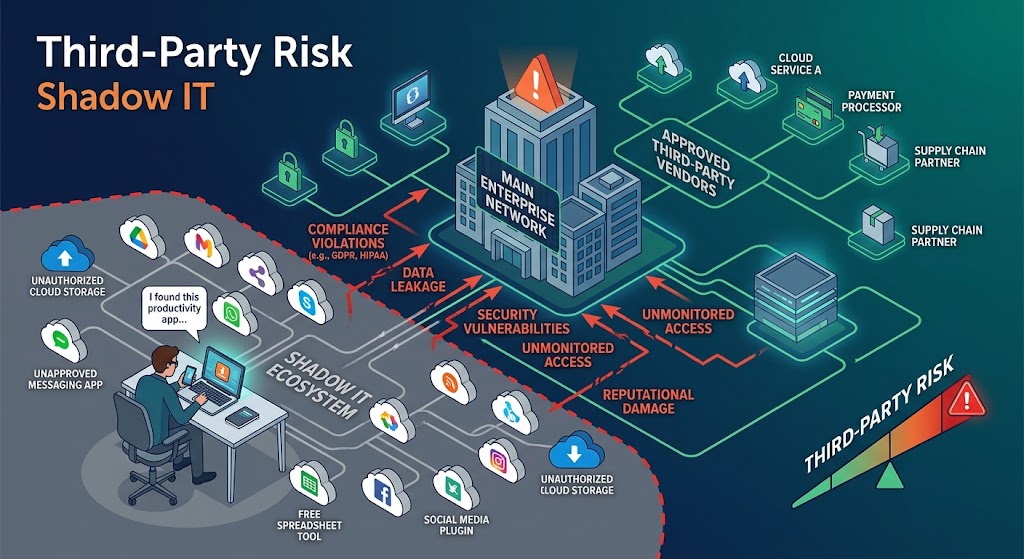
Shadow IT and Third-Party Risk: The Blind Spot Nobody’s Assessing

Shadow IT and Third-Party Risk: The Blind Spot Nobody’s Assessing

Most third-party risk management programs carry a quiet assumption: a vendor only becomes a vendor once procurement knows about it. That assumption is the blind spot itself. Every unsanctioned SaaS tool an employee signs up for with a work email is, functionally, a third party holding company data. It simply never entered the process built […]

AI Governance for Security Leaders: The Policy Framework Your Organization Needs Before the Regulators Ask for It

AI Governance for Security Leaders: The Policy Framework Your Organization Needs Before the Regulators Ask for It

AI Governance for Security Leaders: The Policy Framework Your Organization Needs Before the Regulators Ask for It How to build a practical AI governance program before regulatory pressure forces a rushed response Bola Mabawonku  ·  Senior GRC Manager & Cloud Security Architect  ·  August 2026  ·  8 min read There is a pattern I have […]