Enter your keyword

Third Party Risk

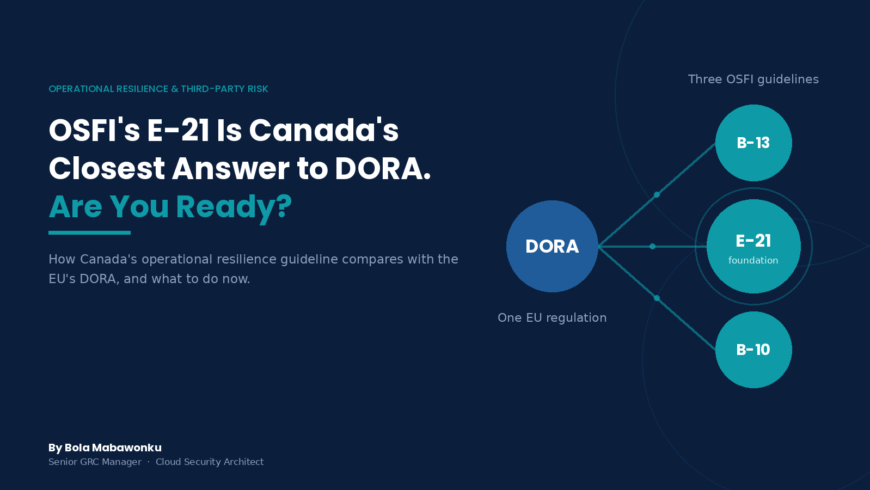
DORA Has a Canadian Cousin. Is Your Resilience Program Ready?

DORA Has a Canadian Cousin. Is Your Resilience Program Ready?

Abstract On September 1, 2026, the Office of the Superintendent of Financial Institutions (OSFI) expected federally regulated financial institutions (FRFIs) to reach full adherence with Guideline E-21, Operational Risk Management and Resilience. E-21 is often described as Canada’s answer to the European Union’s (EU) Digital Operational Resilience Act (DORA), and this article tests that comparison. […]
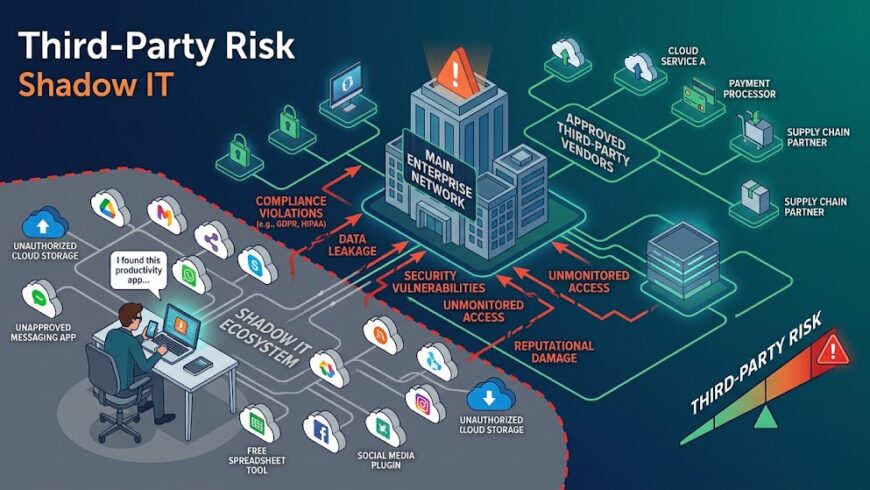
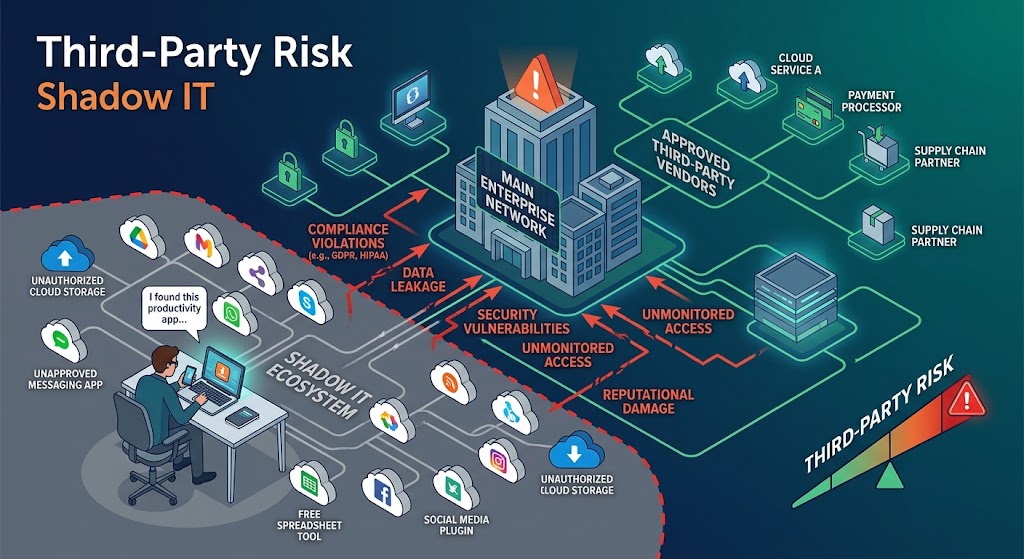
Shadow IT and Third-Party Risk: The Blind Spot Nobody’s Assessing

Shadow IT and Third-Party Risk: The Blind Spot Nobody’s Assessing

Most third-party risk management programs carry a quiet assumption: a vendor only becomes a vendor once procurement knows about it. That assumption is the blind spot itself. Every unsanctioned SaaS tool an employee signs up for with a work email is, functionally, a third party holding company data. It simply never entered the process built […]